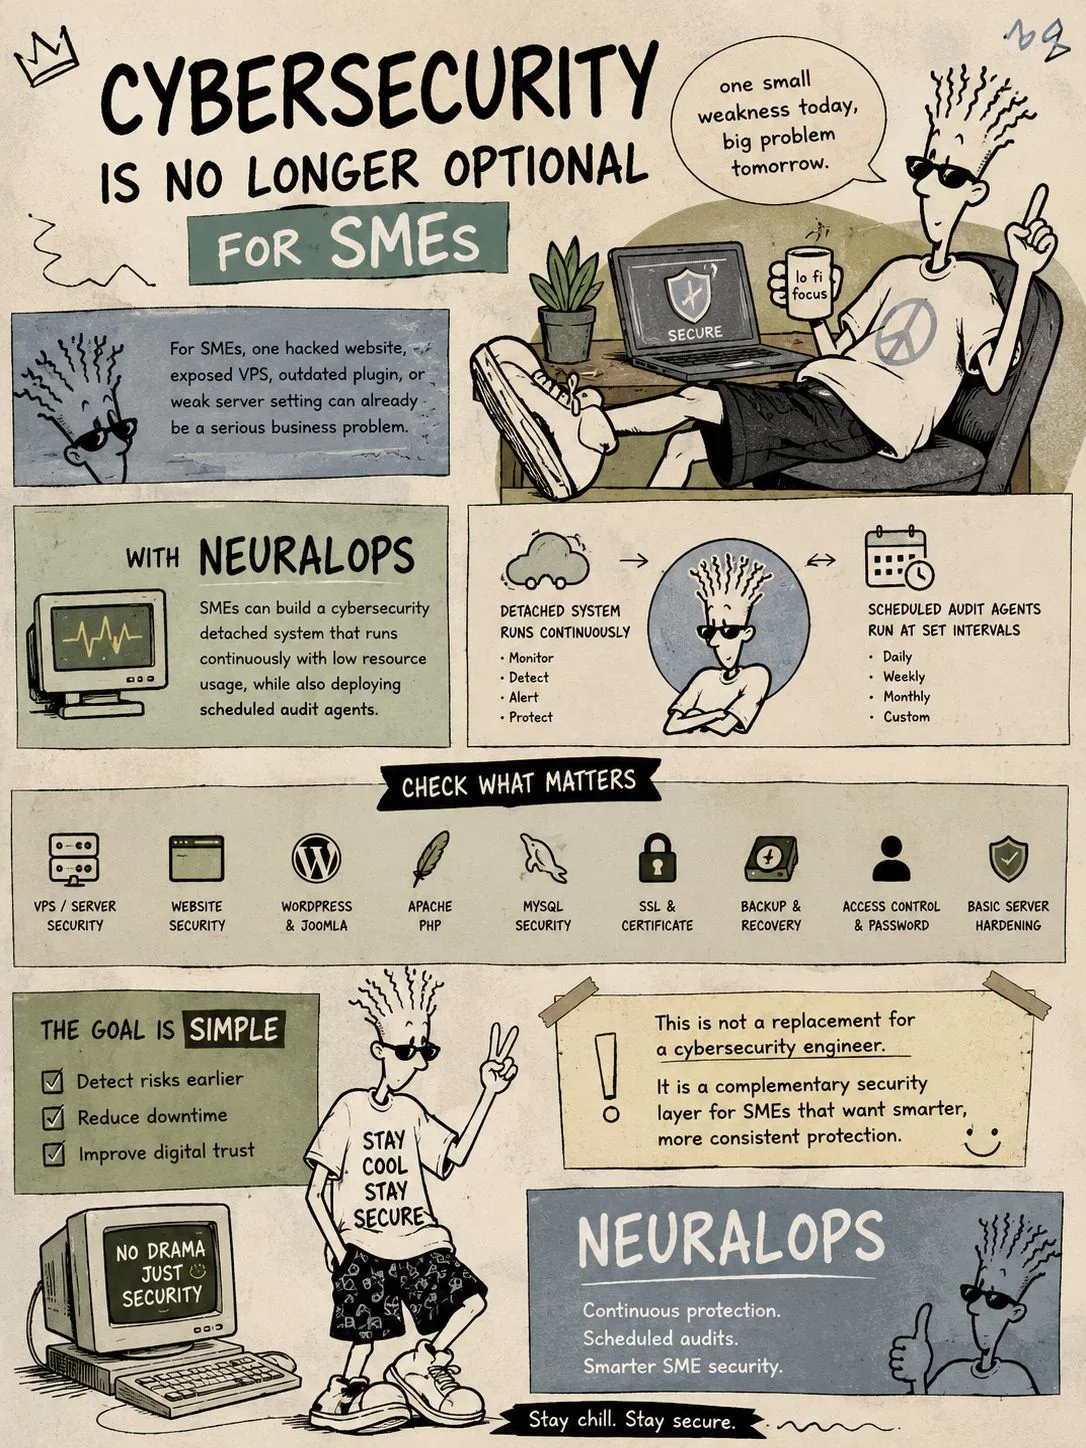
At AINNA, we designed NeuralOps as a practical security layer for this scale. It runs as a detached system with minimal resource overhead, keeping continuous watch while scheduled audit agents inspect the stack you actually operate: VPS, websites, CMS platforms like WordPress and Joomla, Apache, PHP, MySQL, SSL certificates, backups, access controls, and baseline server hardening.
The engineering goal is straightforward: surface risks before they become downtime, and give PKS a clearer signal on digital trust.
This is not a substitute for a dedicated cybersecurity engineer.
It is a complementary, always-on layer that adds consistency to the parts of your infrastructure that are easy to overlook when the team is small and the day is full.
NeuralOps: continuous protection, scheduled audits, and smarter security architecture for PKS.
#NeuralOps #CyberKeselamatan #PKS #DetachedSystem #WebsiteKeselamatan #VPSKeselamatan #WordPress #Joomla #LAMP #PerniagaanContinuity #DigitalTrust
Official Cross-Rangkaian Resource


Ruang pembaca
Apa pendapat anda?
Komen disemak sebelum diterbitkan. Email diperlukan untuk moderasi dan tidak dipaparkan kepada pembaca.
Bagus ada yang tulis pasal surface risks before they become dengan jelas.
First piece I have read that treats surface risks before they become honestly.
Useful. We are dealing with always-on layer that adds consistency right now.
เพิ่งเคยเห็นคนเขียนเรื่องคำอธิบายนี้แบบตรงไปตรงมา
Still thinking about surface risks before they become.
surface risks before they become is the part I would forward to my boss.
Bookmarked, mostly for surface risks before they become.
Clearer than the vendor decks I get about surface risks before they become.