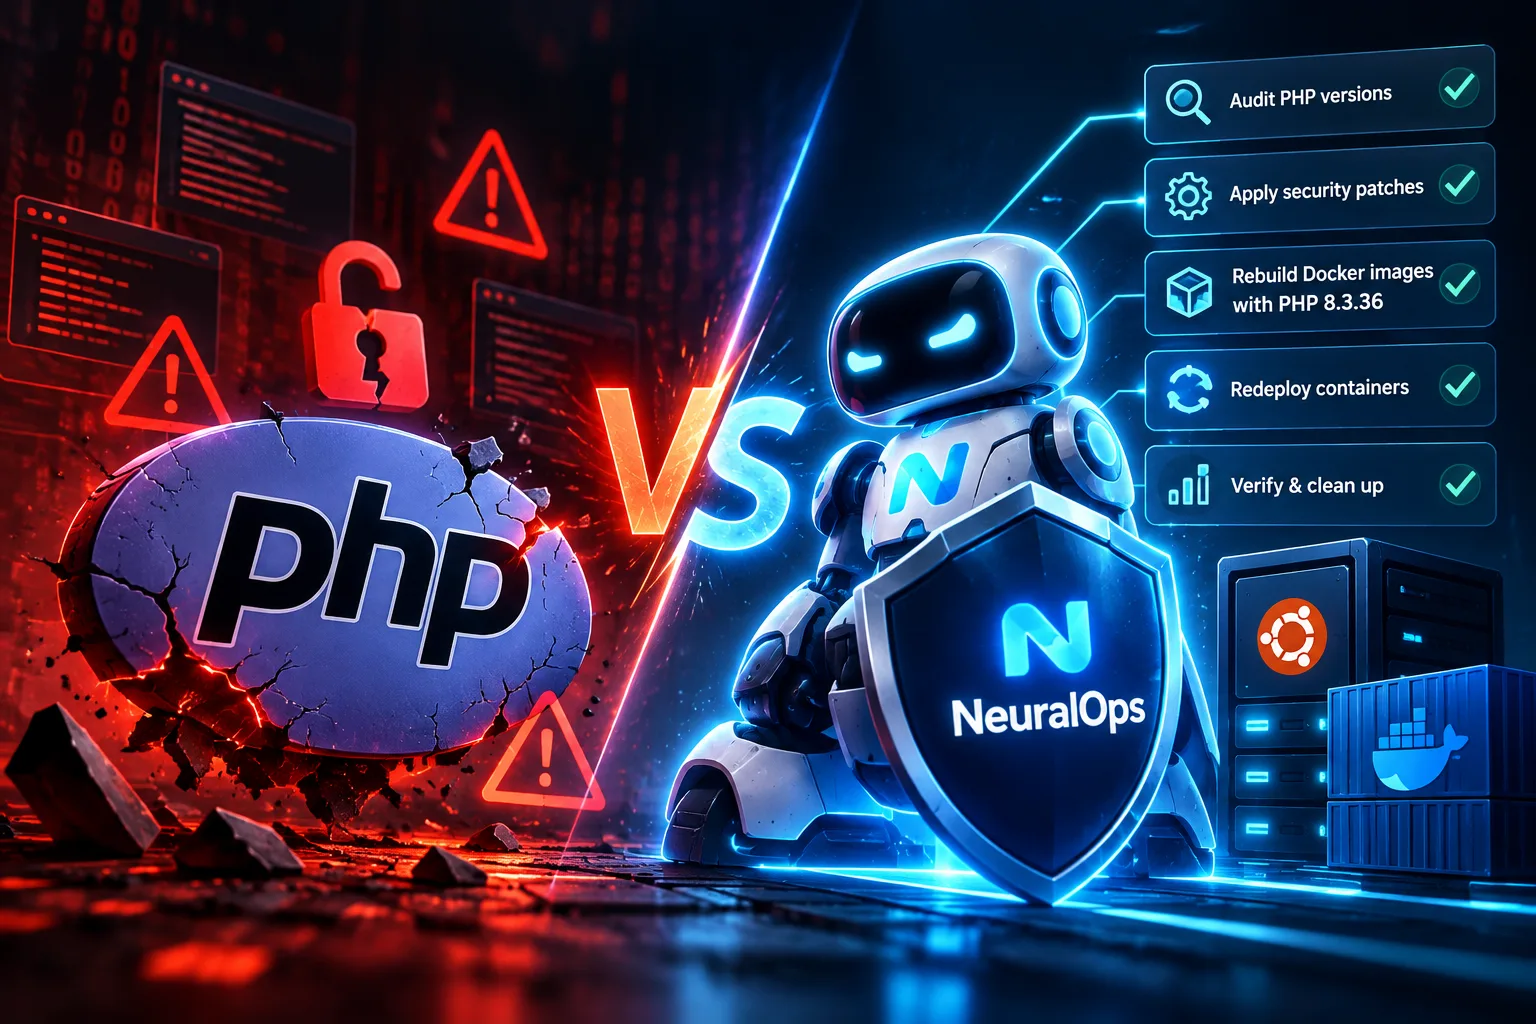
When the latest PHP security advisory landed, I didn't open a terminal and start typing. I scoped the fleet for our Ejen AI, and it worked the problem end to end: audit every server, fingerprint the running PHP versions, flag the vulnerable ones, apply the patches, then prove the stack still held up afterward.
Nobody hand-typed hundreds of Linux commands. We handed over intent in natural language, and the Agent ran the execution chain - inventory, version checks, patch application, automated testing and security validation - with a human sitting at the approval gate for every step that touched production.
That is the shift we are building at AINNA through AINNA NeuralOps. Getting a model to answer a question is the easy half. The hard half is wiring in tool access, guardrails, rollback paths and observability so an agen can act on live systems without becoming the next incident report.
From asking AI to do something, to actually getting things done.
#AgenticAI #AINNA #NeuralOps #PHP #CyberKeselamatan #AIAutomasi


Ruang pembaca
Apa pendapat anda?
Komen disemak sebelum diterbitkan. Email diperlukan untuk moderasi dan tidak dipaparkan kepada pembaca.
अभी भी इस लेख के बारे में सोच रहा हूँ।
Bagus ada yang tulis pasal flag the vulnerable dengan jelas.
Worth reading just for hand-typed.
Useful. We are dealing with getting a model to answer right now.