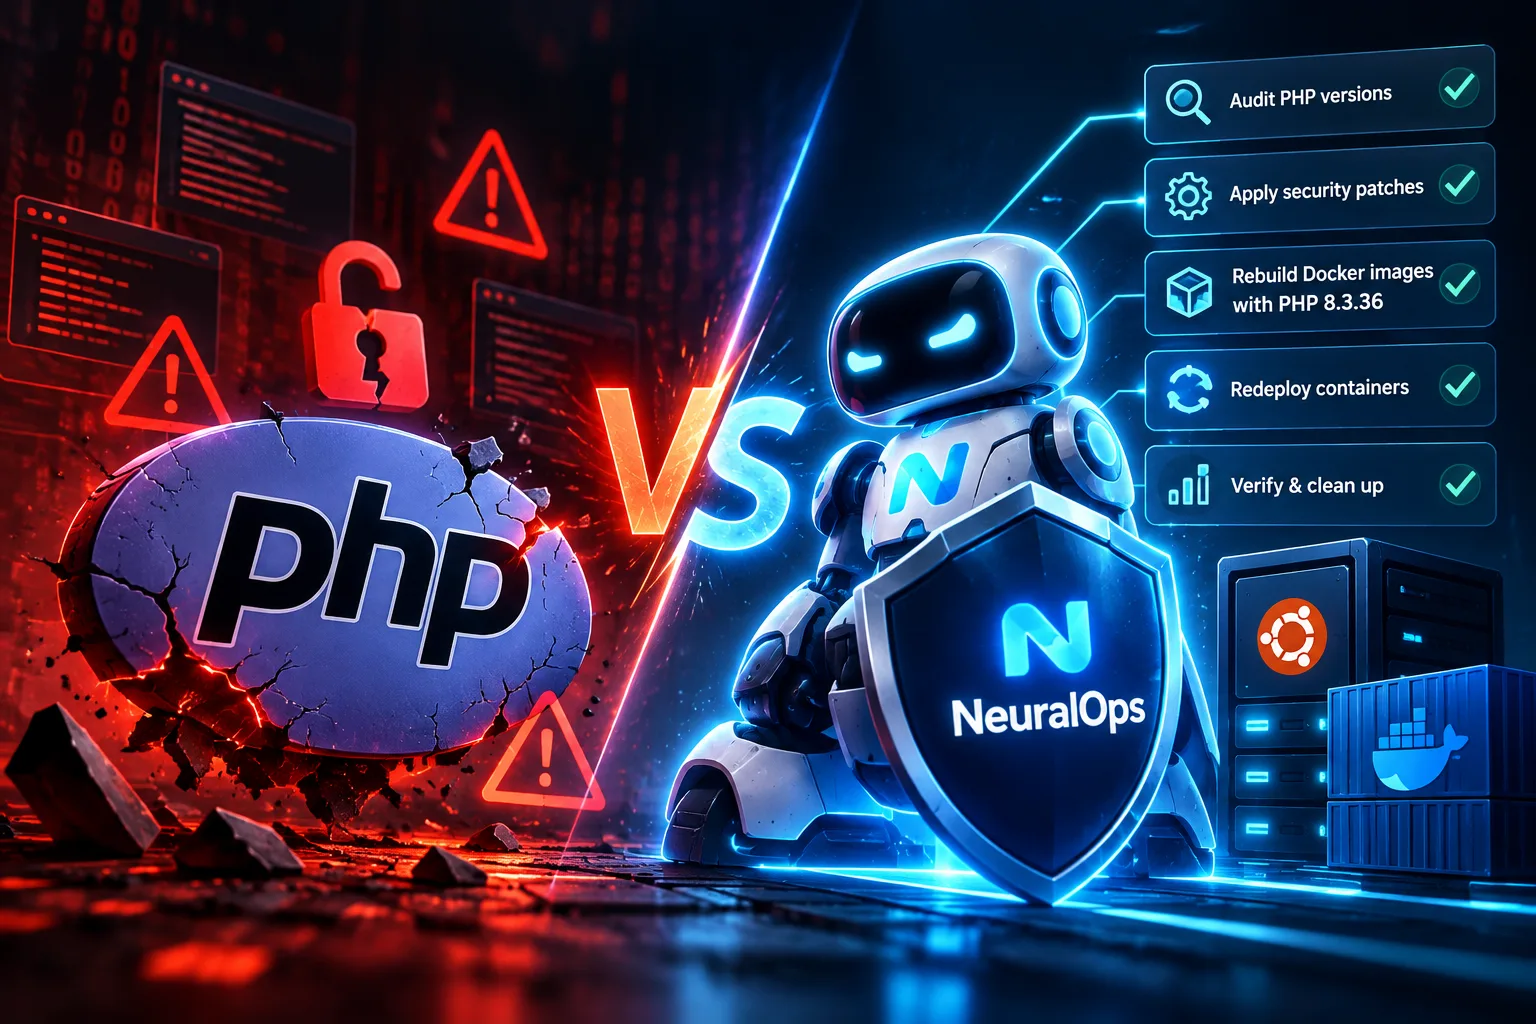
When a PHP security advisory landed on our desk, we treated it the way we treat any other liability: quantify the exposure first, then move to close it. Our instruction to the NeuralOps AI agents was to audit and secure our Ubuntu servers and Docker environments.
Here is what NeuralOps actually executed, and why each step matters on the books:
Audited installed PHP versions and identified affected environments - a fixed-asset register check in practice, so remediation cost was scoped to what was genuinely exposed rather than the whole fleet.
Upgraded Ubuntu PHP security packages - a direct, low-cost remediation instead of a delayed-patch incident carrying far heavier downstream costs.
Rebuilt affected Docker images with PHP 8.3.36 - standardised versions mean predictable support overhead instead of open-ended maintenance spend.
Redeployed affected containers and preserved rollback images - our contingency provision, held in place until verification cleared.
Performed post-patch verification and cleaned up Docker build cache - confirmation that the control worked, plus reclaimed storage that would otherwise sit on the infrastructure bill.
Semua executed through AI agents under human supervision, with safeguards to minimise operational risks - the same internal control logik we apply to any transaction: execution, review and sign-off kept separate.
We set the objective and the risk tolerance. NeuralOps planned and executed the technical work. We supervised, validated and retained the audit trail.
That is what practical AI Ejenik looks like in real IT operations - and, for a Malaysian PKS, what it looks like when an unplanned security cost becomes a closed line item instead of a write-off.
#NeuralOps #AgenticAI #CyberKeselamatan #DevOps #AIAutomasi


Ruang pembaca
Apa pendapat anda?
Komen disemak sebelum diterbitkan. Email diperlukan untuk moderasi dan tidak dipaparkan kepada pembaca.
Bahagian quantify the exposure first tu yang buat saya fikir lama.
Angka tentang quantify the exposure first lebih masuk akal daripada kebanyakan pos.
I read this twice. Redeployed affected containers and preserved is the part that stuck.
Sent this to two people already. Upgraded ubuntu PHP security packages is why.